Authorized Actions Can Still Create Unauthorized Outcomes.
AIS Connects Permissions, Purpose And Combined Consequences Across Agent Activity.
AI Trust, Security And Governance
Protect AI Agents, Models, Tools And Memory. Govern Their Decisions, Preserve Trusted Context And Keep Safe Work Moving As AI Changes.
In Development
Target Release: 30 November 2026
Designed Around The Mission, Its Evidence And Its Consequences.
Six Signature Mechanisms Protect More Than A Single Interaction: They Keep Confidence Grounded, Context Clean And The Mission Moving Safely.
Evaluate Combined Actions Across Agents And Branches, Including Consequences That An Isolated Tool Call Can Conceal.
Keep Source Origins, Authorized Scope And Independently Observed Effects Connected. Repeated Claims Do Not Create Independent Proof.
Contain Contaminated Paths And Continue Only Within Verified Safety And Existing Authority. Stop Or Escalate When Safe Continuation Cannot Be Established.
Connect Accountable Ownership And Lifecycle Policy To Immunity. Qualify New Guardrails Against Attacks And Legitimate Work, Authorize Promotion And Refresh Affected Trust Evidence.
AIS Protects Its AI Domain Independently. AS-OS Brings The Enterprise Operating Model: Business Context, Better Decisions, Coordinated Response And Continuity Across Your Security Operations.
Stop Repetition From Becoming False Confidence. Verify Intent Against Real Effects. Catch Combined Harm, Clean Contaminated Context, Preserve Safe Work And Refresh Trust As Your AI Changes.
Keep The Source Behind Every Claim.
Trace Origins Across Copies, Summaries And Agents. Repeated Derivatives Of One Source Do Not Become Independent Confirmation.
Five Agents Quoting One Document Still Equal One Source.
Five Agents Repeat The Same Poisoned Document. AIS Is Designed To Preserve Their Shared Origin So Repetition Cannot Be Mistaken For Independent Support.
Illustrative Scenario · Planned Product Design
Check What The Action Actually Did.
Compare The Authorized Target And Scope With The Separately Observed Effect. A Success Message Alone Does Not Establish The Result.
An Allowed Read Must Not Silently Export Customer Data.
An Agent Is Allowed To Read A Customer Record. The Relevant Question Is Whether The Observed Effect Stayed Within That Read Or Sent The Data To A Different Destination.
Illustrative Scenario · Planned Product Design
See The Harm Across The Whole Task.
Evaluate Cumulative Access, Authority And Effects Across Agents And Concurrent Branches. Splitting A Harmful Objective Does Not Reset Its Limits.
Two Allowed Reads Must Not Combine Into Prohibited Disclosure.
Two Agents Read Different Parts Of A Sensitive Dataset. The Combined Result Must Still Respect The Task’s Disclosure Boundary.
Illustrative Scenario · Planned Product Design
Remove The Poisoned Path.
Trace And Quarantine Contaminated Memory, Summaries And Dependent Branches While Preserving Trustworthy Context.
Preserve Unaffected Work While Cleaning Contaminated Context.
A Poisoned Retrieval Enters A Summary And Then An Agent’s Memory. The Cleanup Must Follow Those Dependencies Instead Of Treating Each Copy As A Separate Source.
Illustrative Scenario · Planned Product Design
Protect The Work Worth Continuing.
Continue Only Work That Remains Verifiably Safe Within Its Existing Authority. Stop Or Escalate When No Safe Continuation Exists.
Contain The Risky Branch While Safe Work Continues.
One Branch Of A Multi-Agent Task Is Compromised. Unaffected Work May Continue Only When Its Safety And Existing Authorization Can Still Be Established.
Illustrative Scenario · Planned Product Design
Keep Trust Bound To The Current Version.
Bind Assurance To Model, Tool, Permission And Context Versions. Recheck Evidence Affected By A Relevant Change.
Yesterday’s Approval Does Not Certify Today’s Changed Agent.
A Tool Gains New Permissions After An Evaluation. The Evidence Affected By That Change Must Be Re-Evaluated Before The Old Approval Is Relied On.
Illustrative Scenario · Planned Product Design
Protect The Whole AI Estate.
Discover What Is Connected. Protect Models, Agents, Memory, Tools And Enterprise Resources. Detect Harmful Activity And Constrain Its Consequences.
Discover Models, Apps, Agents, Tools And Dependencies. Map Owners, AI Bills Of Materials, Permissions, Trust Boundaries And Attack Paths.
Trace Human-To-Agent And Agent-To-Agent Authority. Expose Excessive Privileges, Token Misuse And Escalation; Bind Actions To Current Permissions.
Detect Direct And Indirect Injection, Jailbreaks And Task Hijacking Across Supported Text, Documents, Images, Audio, Code And Tool Responses.
Authorize Retrieval Sources, Preserve Integrity And Lineage, And Contain Poisoned Memory, Manipulated Instructions And Dependent Context.
Inspect Tool Definitions, Skills, Permissions, Arguments And Changed Behavior. Check Model And Component Provenance, Integrity And Supply-Chain Risk.
Protect Model And Package Integrity, Personal Data, Secrets And Intellectual Property. Govern Outputs, Data Access And Exfiltration Destinations.
Exercise Bounded Multilingual, Multi-Turn, Multimodal And Multi-Agent Attacks. Constrain Recursive Loops, Runaway Delegation And Resource Abuse.
Detect Purpose Drift, Task Hijacking And Cross-Agent Abuse. Block Calls, Revoke Access, Quarantine Context And Verify Containment Effects.
Own Every AI Decision.
Connect Accountable Ownership, Purpose And Risk Decisions To Operating Controls As AI Use Changes.
Governance Continues Through Change And Retirement.
Register Use Cases, Accountable Owners, AI Assets, Intended Purpose And Risk Boundaries.
Assess Risk, Record Approvals And Time-Bound Exceptions, And Require Review After Relevant Changes.
Preserve Technical Evaluation Results, Their Limits And The Evidence For The System Version Under Review.
Link Approved Policy To Enforcement And Monitoring, With Visible Coverage And Gaps.
Invalidate Stale Assurance, Re-Evaluate Changes And Govern Evidence Retention And Decommissioning.
Trust The Evidence. Verify The Effect.
Evaluate Origins, Combined Consequences And Observed Outcomes Against The Relevant Model, Tool, Permission And Context Versions.
Five Agents Repeating One Document Still Represent One Source. Preserve Causal Origins Across Copies, Summaries And Memory.
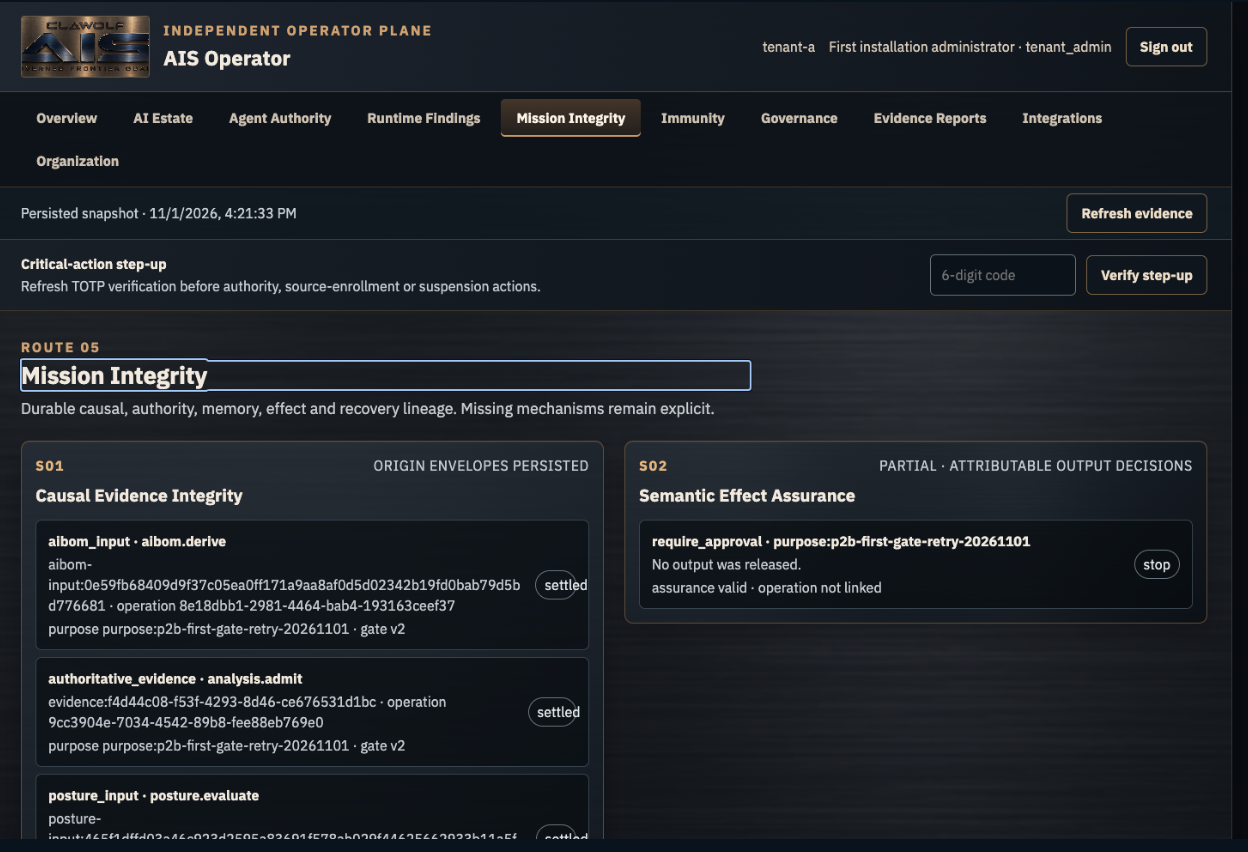
Causal Evidence IntegrityCompare Authorized Scope With The Separately Observed Effect. Evaluate Combined Outcomes Across The Task.
Semantic Effect AssuranceA Changed Tool Or Permission Can Invalidate Earlier Assurance. Re-Evaluate The Evidence Affected By That Change.
Continuous Assurance Invalidation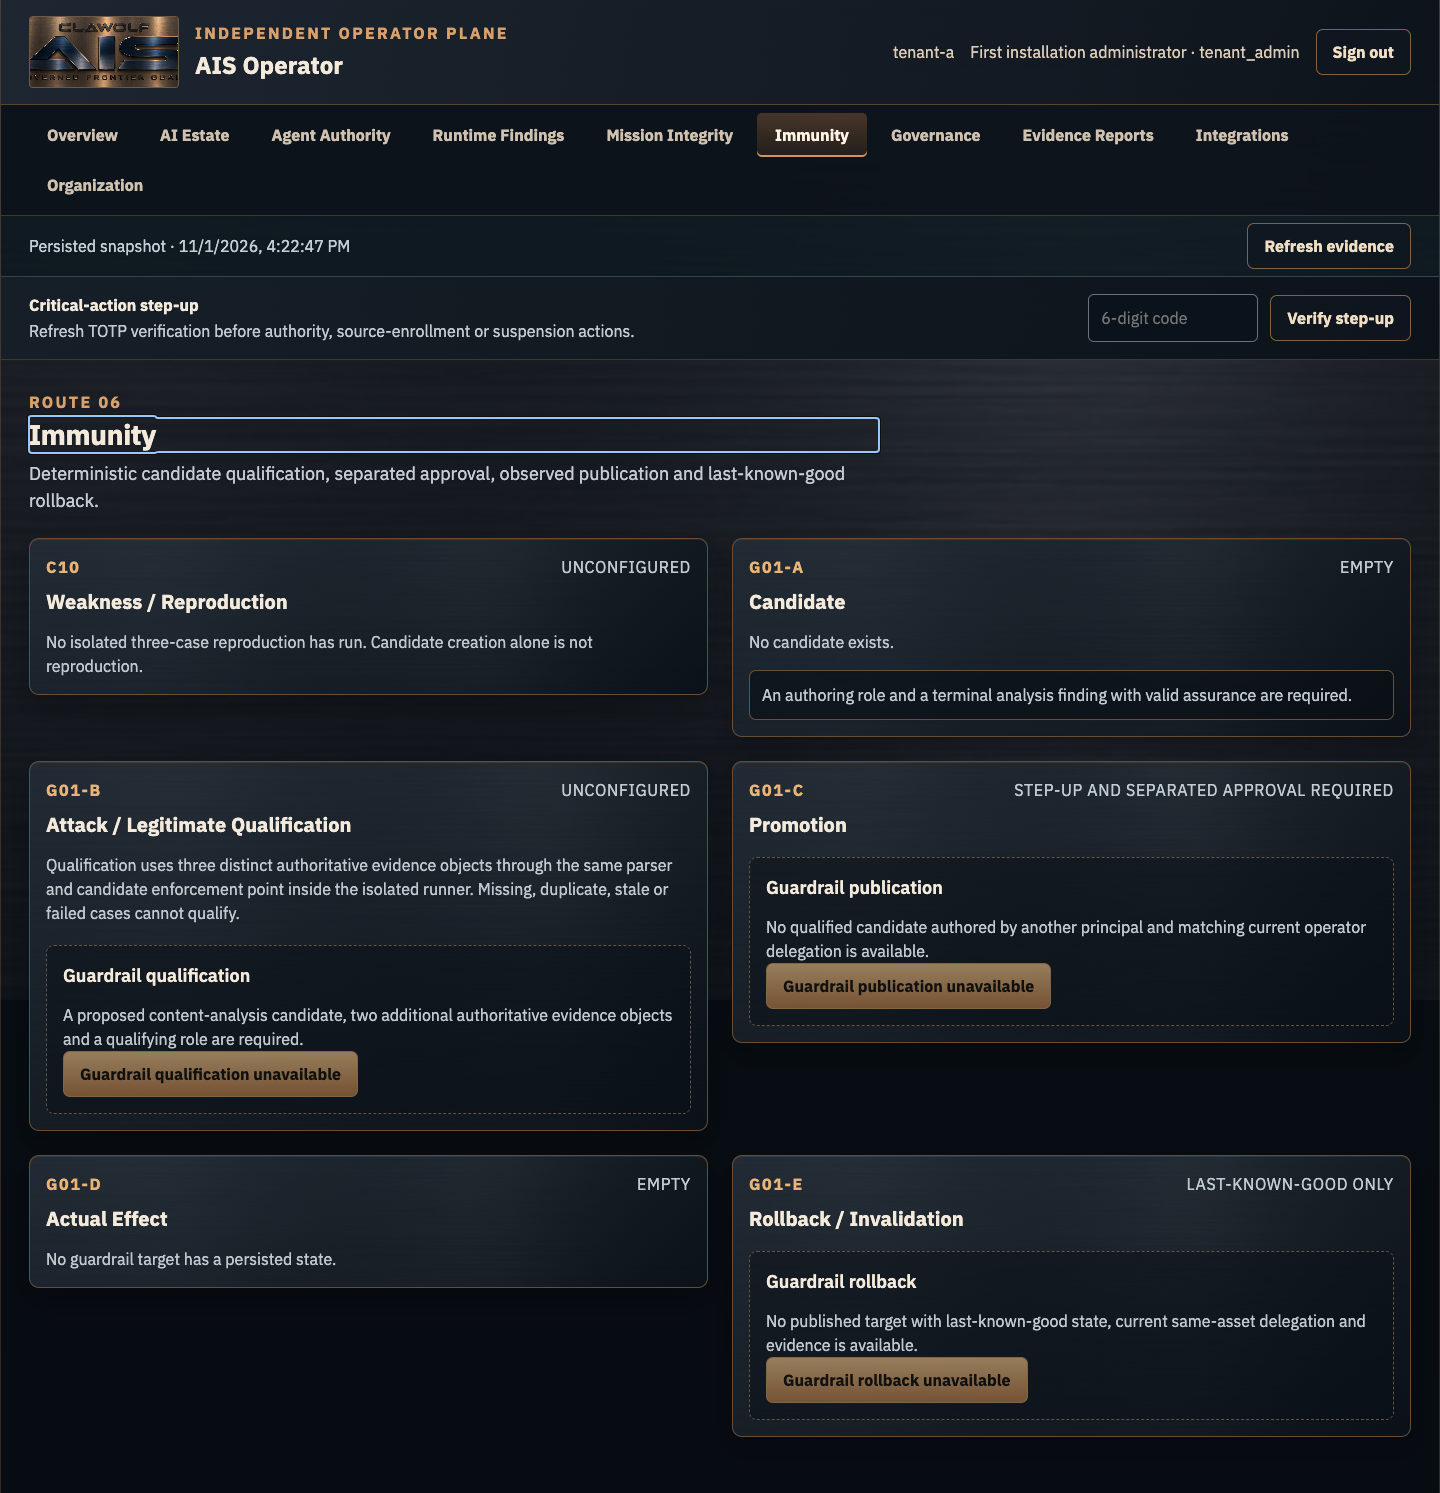
Turn Weaknesses Into Qualified Protection.
Governed Guardrail Engineering Connects Reproduced Weaknesses To Tested, Authorized And Recoverable Protection.
Reproduce A Genuine Weakness Within An Authorized, Bounded Scope.
Derive A Constrained Guardrail. Generation Does Not Grant Permission To Activate It.
Test Original And Held-Out Attacks Alongside Legitimate Tasks And The Intended Operating Scope.
Apply Policy, Approval And Delegated Authority To The Exact Protection Version And Target.
Independently Observe The Protective Effect. Restore And Verify The Last Known Good Version When Necessary.
Re-Evaluate Affected Assurance And Retain Finding, Qualification, Authorization And Outcome Lineage.
Qualification Must Preserve Legitimate Work As Well As Resist Attacks. Promotion Requires The Assigned Authority; Actual Protective Effects And Recovery Must Be Verified.
Deploy AIS Independently For AI Protection. Choose Native AIS + AS-OS To Connect That Defense To Enterprise Security Operations.
AIS Owns AI-Domain Analysis, Governance, Authorized Protection And Recovery. No AS-OS Runtime Or License Is Required.
AS-OS Connects Detection, Decision, Action, Control And Learning Across The Enterprise. AI-Domain Protection Becomes Part Of A Coordinated Response That Preserves Business Continuity.
Explore AS-OSAIS Protects AI And Agent Activity. AIS + AS-OS Connects That Protection To Institution-Wide, Coordinated Security Operations With Outcome Evidence.
Separately Adopted CNDA Products Add Identity, Data, Behavior, Insider, Supply-Chain And Cloud Context As The Portfolio Develops. Explore The Roadmap
Tell Us About Your Agents, Data And Business Priorities. We’ll Show You The Relevant AIS Capabilities And Discuss Your Standalone Or Native AS-OS Path.